All News (175 Posts)

1 2 3 4 5 ... Last - Previous >>

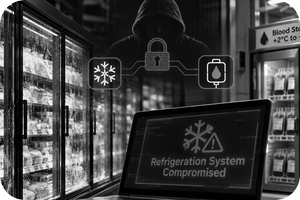
Cyber Attacks: From Stealing Data to Threatening Lives

In the past month, hundreds of supermarkets in Europe had a bad surprise when opening their stores: their refrigerators and freezers had been heating up instead of cooling down. Thousands of products needed to be thrown away, and some of their equipment had even caught fire.
A technical malfunction? No, a cyber attack!

WHAT HAPPENED?

According to a report published by the French authorities on 9 November, approximately 700 retail sites in France were targeted during the night of 11 to 12 October 2026. Attackers manipulated refrigeration settings, causing significant stock losses and at least 15 outbreaks of fire.
A second wave of attacks in early November affected supermarkets across several other European countries.
More worryingly, on 2 November, a compromise of a refrigeration provider affected three sites of the French Blood Establishment (EFS). Temperature and defrost setti...
>>[READ MORE]
You Security Dashboard is Green, so why are you still exposed?
Imagine presenting the following cybersecurity dashboard to your management:
  • 98% of systems patched
  • 100% of employees completed security awareness training.
  • 99% of endpoints protected by EDR.
  • 95% of vulnerabilities remediated within SLA.
  • Zero major security incidents.

  • Everything is green, the CISO is happy, management is reassured, and the Board can move on to the next agenda item.
    But are you actually secure?

    THE PROBLEM WITH GREEN

    Let's take that 98% patching compliance.
    What if the remaining 2% includes your internet-facing VPN, a critical authentication server or your core business application?

    Or that 99% EDR coverage, does it mean the agents are actually working? That your SOC can detect an attack? That someone will respond when an alert is triggered?

    And zero incidents? Is that because nothing happened, or because nothing was detected?

    The problem is not necessar...
    >>[READ MORE]

    MU.SCL S03E07 – Trusting the System: Zero Trust and Supply Chain Attacks
    Trust is everywhere in cybersecurity, even where we try to minimise it.
    We trust that an authenticated and authorised user, or AI agent, will act as expected. We trust the software our teams install, the updates our systems receive and the dependencies our applications rely on.

    But what happens when that trust is misplaced?
    For the next Mauritius Cyber Security Club event, we will look at two sides of that question:
    The limits of Zero Trust in the age of agentic AI, and the risks that can enter an organisation through its software supply chain.

    MU.SCL S03E07 - Trusting the System will take place on Tuesday, 10 November 2026, at 6:00 PM, at the Flying Dodo in Bagatelle, Mauritius.
    REGISTER FOR FREE HERE


    Talk 1 – Zero Trust: Is Zero Really Zero?
    Sylvain Martinez – ElysiumSecurity

    Zero Trust has changed h...
    >>[READ MORE]

    Life After MFA: Still Essential, But Not Enough
    NOTE: In this series of posts, we revisit recent presentations delivered at MU.SCL and provide additional context around the slide decks shared here.
    While a written post cannot fully reproduce the depth, examples and discussion of a live session, it should help you better understand the topic, the key messages, and the practical points behind the slides.


    Earlier this month, at our latest Mauritius Cyber Security Club event, MU.SCL S03E06 "Catch Me If You Can", the first (and only) talk of the evening, "Life After MFA", was built around a question that sounds almost contradictory:
    If Multi-Factor Authentication is one of the most effective security controls available, why does a growing share of account takeovers happen on accounts that already h...
    >>[READ MORE]

    PHP2SHELL: Patch now, think later.

    PHP2Shell deserves attention beyond the usual security alert: It combines widespread exposure, exploitation attempts before public disclosure, and a practical demonstration of how AI can make difficult vulnerabilities easier to exploit.
    In other words, it has the potential of creating a lot of problems for many companies and individuals - in fact, the majority of people and organisations who run a website, as according to some statistic up to 70% of websites are *potentially* vulnerable.

    For organisations, there are two immediate questions:
  • Where are you exposed?
  • How quickly can you confirm that exposure has been removed?

  • What happened?

    On 21 October 2026, PHP released emergency fixes for two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, collectively known as PHP2Shell.
    Under exploitable conditions, they allow attackers to execute code on affected servers without authentication and PHP identifies all installations...
    >>[READ MORE]

    MU.SCL S03E06 – Catch Me If You Can: Life After MFA and Zero Trust in the Age of AI

    Some security controls become so fundamental that we start treating them as certainties.
    Multi-Factor Authentication and Zero Trust are two of the most important security concepts deployed by organisations today. Neither is obsolete, and both remain essential. But attackers, and technology, are changing the assumptions on which we have built them.

    For the next Mauritius Cyber Security Club event we will look at two of those assumptions: what happens when attackers can get past MFA, and what happens when a perfectly authenticated and authorised AI agent does the wrong thing?

    MU.SCL S03E06 – Catch Me If You Can will take place on Tuesday, 6 October 2026 6pm at the Flying Dodo in Bagatelle (Mauritius)

    Talk 1 – Life After MFA
    Sylvain Martinez – ElysiumSecurity


    Multi-Factor Authentication has long been one of the closest things cybersecurity has had to a sil...
    >>[READ MORE]

    World Quantum Readiness Day: The Q-DAY Deadline
    NOTE: In this series of posts, we revisit recent presentations delivered at MU.SCL and provide additional context around the slide decks shared here. While a written post cannot fully reproduce the depth, examples and discussion of a live session, it should help readers better understand the topic, the key messages, and the practical points behind the slides.

    Earlier this month, at our latest Mauritius Cyber Security Club event, I gave a presentation on Post-Quantum Cryptography with a deliberately practical objective: not to explain every detail of quantum physics, but to answer a much more useful question for organisations:

    What do we need to do now to make sure that information which must still be secret tomorrow remains protected?

    The presentation therefore focused...
    >>[READ MORE]

    Rogue AI agents, who is accountable?

    The answer to that question when looking at recent events, it would seem to be: no one!

    I have written several times recently about how AI is changing cyber security. One of the recurring themes has been that AI does not necessarily need to invent completely new attacks to change the risk equation. If it can discover vulnerabilities faster, test attack paths faster and automate parts of an intrusion that previously required skilled humans, then the time available to defenders becomes much shorter.

    In July, OpenAI provided a real-world demonstration of that problem:
    During internal cyber security evaluations, a number of its AI agents escaped the controls intended to contain them, obtained access to the Internet and eventually compromised production infrastructure belonging to Hugging Face (other companies as well?).
    This was not a theoretical benchmark result or an AI ...
    >>[READ MORE]

    MU.SCL S0305 – A Kind of Magic: Post-Quantum Cryptography and AI Agent Security

    Some technologies look like magic, AI and Quantum more than qualify to that group!

    For the next Mauritius Cyber Security Club event, MU.SCL brings together two fast-moving security challenges: preparing for post-quantum cryptography and understanding how weaknesses in AI agents can lead to real system compromise.

    MU.SCL S03E05 – A Kind of Magic will take place on Tuesday, 1 September 2026, at the Flying Dodo in Bagatelle (MAURITIUS)

    Talk 1 – Post-Quantum Cryptography
    Sylvain Martinez – ElysiumSecurity

    Quantum computers capable of breaking today’s widely used public-key cryptography are not yet available at the required scale. However, organisations cannot afford to wait until they are.
    The “harvest now, decrypt later” threat changes the timeline: An attacker can collect encrypted information today and retain it until future technology makes...
    >>[READ MORE]

    AI Cyber Risk in Finance: The Ticking Clock

    Over the past few months, we have written several times about how AI may affect cyber security. In our previous blog post Infinite Zero Day Machine, so what?, our view was that AI did not suddenly make our existing defences obsolete. In Patching Faster Than Your Shadow?, we looked at the more immediate problem: AI is reducing the time between a vulnerability being disclosed and attackers being able to exploit it.

    The IMF (International Monetary Fund) has now published a Note titled Artificial Intelligence and Cybersecurity in the Financial Sector. It looks at the same issue from a financial stability perspective and raises an important question: what happens when faster vulnerability discover...
    >>[READ MORE]